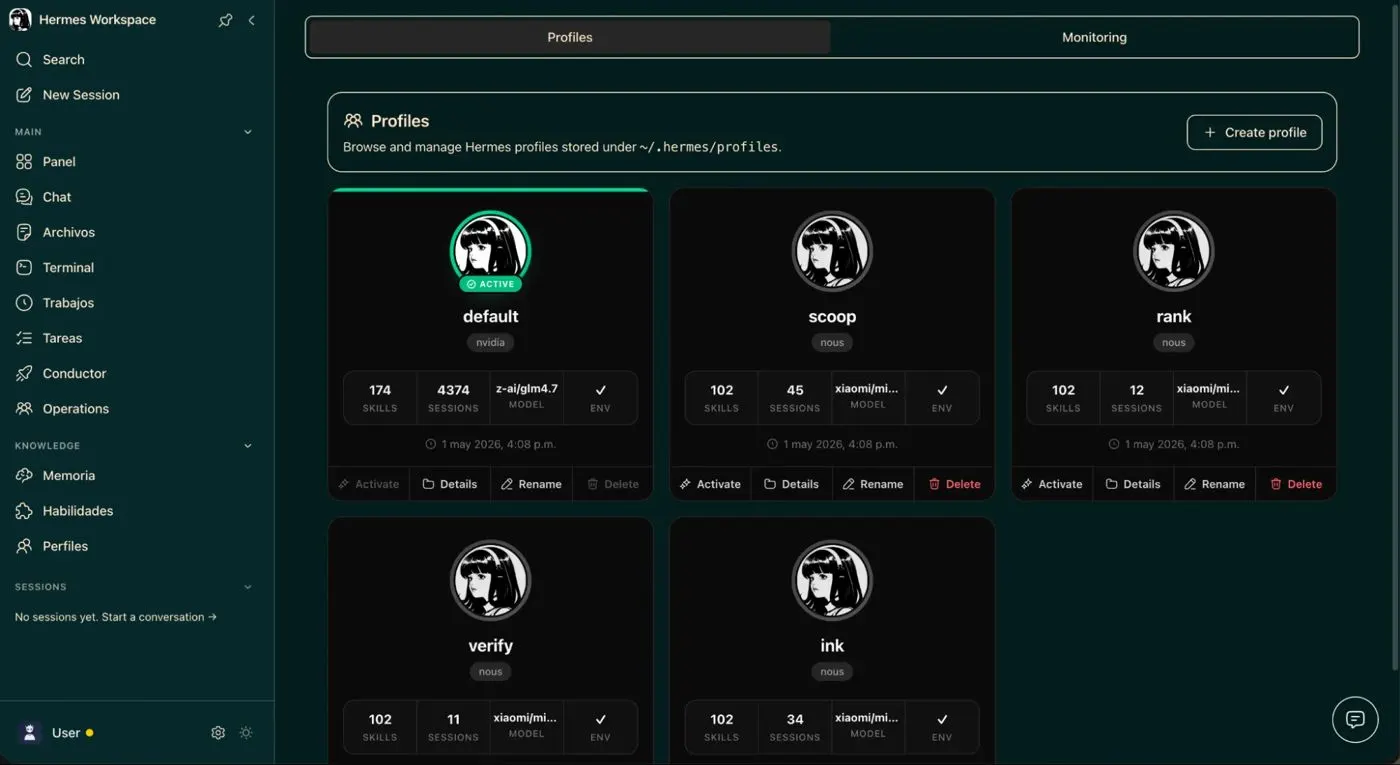
Hermes Agent is a free, self-improving personal AI agent from Nous Research. It runs on the user's computer or server, keeps long-term memory, writes reusable skills from tasks it has already done, and takes actions, including browsing, on command from chat apps like Telegram, Slack and WhatsApp. Tech Times dates its public launch to Feb 25, 2026, and it is MIT-licensed on macOS, Windows, Linux and Android, with optional Nous Portal cloud plans.
It grew fast. Tech Times reported in May 2026 that Hermes had passed OpenClaw as the most-used open-source agent on OpenRouter's token rankings, and the GitHub repository had about 253,600 stars on Nov 1, 2026. On May 20, 2026 it gained native access to a hub of 400+ site-specific browser skills built by Browserbase, covering marketplaces, travel and government sites.
Those saved skills are what make Hermes interesting to a fraud team. Once a skill exists for a site, running the same task again is cheap, which is great for one person's weekly errand and just as useful to someone repeating the same sign-up or listing flow hundreds of times.
How Hermes Agent shows up on your site
Hermes has no web identity of its own, so what reaches you is whatever browser it is configured to use. Its browser docs list a local headless Chromium with a throwaway profile as the default. It can instead snapshot the user's real browser profile, attach to their own Chrome, Edge or Brave over the DevTools Protocol, or use cloud browsers from Browserbase, Browser Use, Firecrawl or the Nous Tool Gateway. Before Mar 7, 2026, browsing required a Browserbase key, so early Hermes traffic came through Browserbase.
| Check | What Hermes Agent does |
|---|---|
| User agent | No Hermes token. It sends whatever its browser sends |
| Web Bot Auth signature | Hermes does not sign. Browserbase, a Cloudflare signed agent, signs only if that customer turns it on |
| IP ranges | No list. Home IP locally, proxies in cloud mode |
| robots.txt | Not documented |
Why Hermes Agent is hard to detect
The default mode is not hard, because a local headless Chromium shows the standard headless and DevTools automation markers. The difficulty is that a Hermes user can change modes with one setting. In attach mode it drives the user's real Chrome with genuine fingerprints on a home IP, and its own docs describe the profile snapshot as a convenience rather than an isolation boundary, so the site is effectively talking to the person's browser.
Cloud mode moves the problem to the browser host. Hermes's docs say the Browserbase and Browser Use backends add stealth, random fingerprints and CAPTCHA solving by default, so those sessions look like ordinary Chrome on residential IPs. Browserbase was in Cloudflare's first cohort of signed agents in Aug 2025, so its signed sessions can be verified, while unsigned ones leave behavior as the main tell: instant typing, no mouse movement and burst scrolling. Skill replays also follow identical selectors and request sequences, so many accounts walking the exact same path can stand out.
How Verisoul detects Hermes Agent
Verisoul does not name Hermes, because Hermes declares nothing. It names the browser Hermes is using. Local headless runs show headless browser markers or DevTools-protocol automation artifacts plus scripted navigation, and come back as headless_chrome or cdp_automation. Browserbase sessions that carry a verified signature come back as browserbase. Attach-mode and unsigned stealth sessions are flagged through bot score without an agent name.
"agent": {
  "id": "headless_chrome",
  "name": "Headless Chrome",
  "provider": "Open source",
  "type": "headless_automation",
  "detection_method": "self_declared",
  "detection_signals": [
    "network",
    "device",
    "behavioral"
  ]
}idis the identifier for rules, hereheadless_chrome; the same session could also becdp_automationorbrowserbasedepending on the backendtypeisheadless_automation, a scripted browser with no person at the controlsdetection_methodisself_declared, meaning the browser exposed its own automation markersdetection_signalsshows the evidence,devicefor headless or DevTools artifacts andbehavioralfor scripted navigation
Agent Atlas has entries for Headless Chrome, DevTools automation and Browserbase, and the AI agent detection docs explain the response fields.
- 01User asks Hermes on Telegram
- 02Hermes runs a saved site skill
- 03Local headless Chromium opens your page
- 04Your page sees headless markers
How to detect Hermes Agent step by step
- Add the Verisoul SDK to sign-up, login and payout pages using the Verisoul docs
- Handle
headless_chromeandcdp_automationwith your automation rules, andbrowserbasewith a separate rule for signed hosted sessions - Watch for many accounts following an identical page path and timing, which is what replayed skills look like
- Review high bot score sessions with no agent name, since attach-mode Hermes lands there
Should you block Hermes Agent?
Hermes often acts for one real person, and on public browsing pages there is little to gain from blocking it. At sign-up and payouts the cost of a skill-driven repeat run is close to zero, so most teams block headless_chrome and cdp_automation on those steps.
Signed browserbase sessions are honest about being hosted automation, which makes them reasonable to allow while browsing and to send to review at sign-up, checkout or payouts, because the signature identifies the host and not the person behind it.